Product
What Surfacia does
Surfacia is an Attack Surface Management platform. It continuously maps every domain, subdomain, IP, port, endpoint and cloud asset your organisation exposes to the internet, finds the weaknesses on them, and shows how it all connects, so your team knows what to fix first.
Inside the product
Inside the product
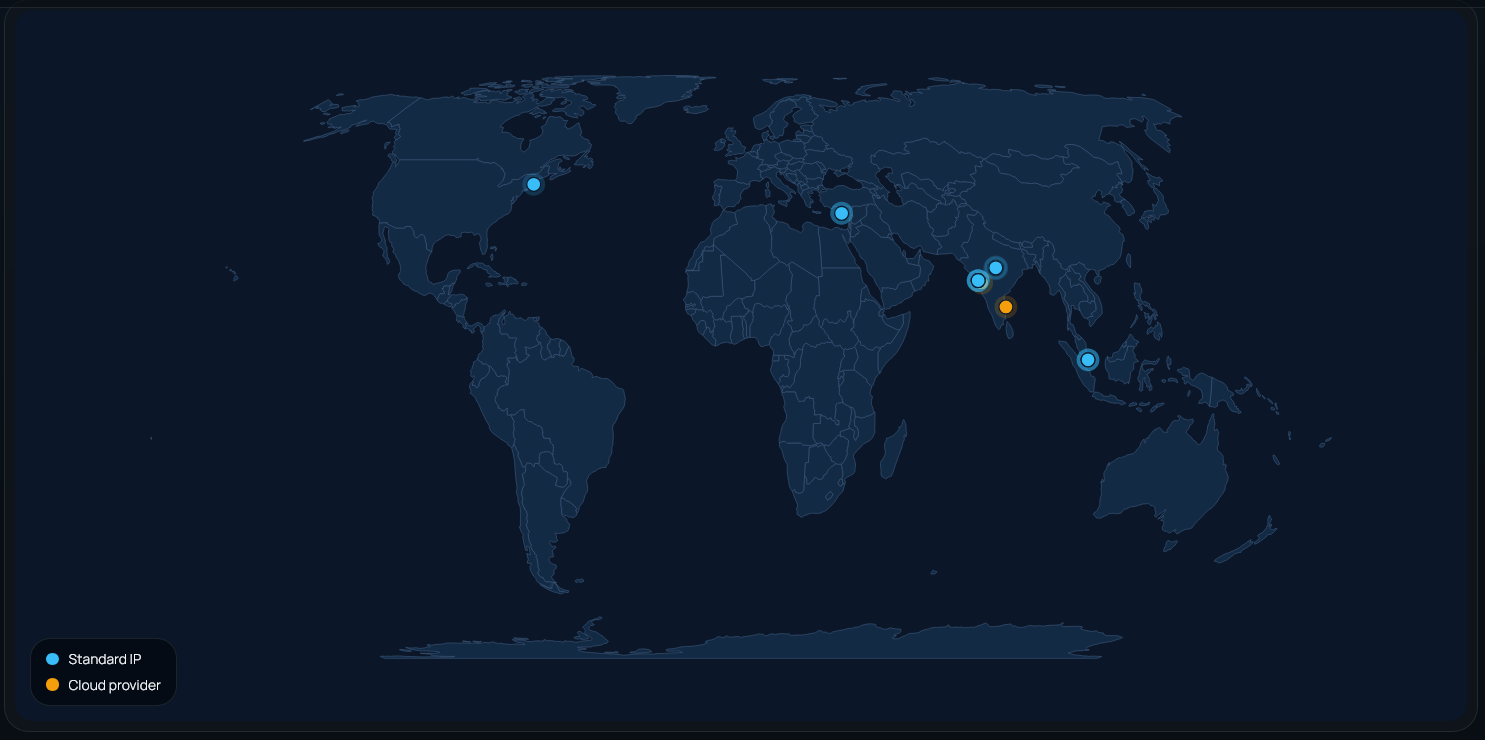
Attack-surface graph
A visual map of how assets, services and findings relate to each other.
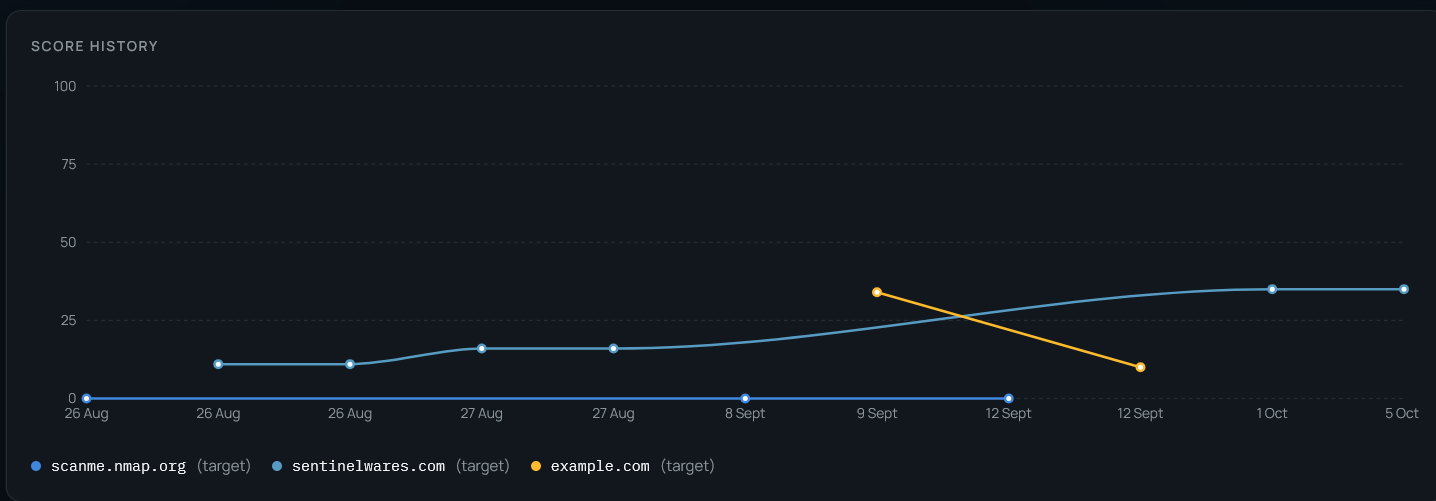
Risk trend chart
See whether your exposure is shrinking or growing over time.
Activity logs and alerts
Activity logs and alerts for transparency and staying updated for your attack surface.
Interlinked JSON export
One file per target with all recon data cross-referenced, for your own tools and automation.
Team access
Invite colleagues and clients with role-based access.
Coverage
Beyond the perimeter you already know.
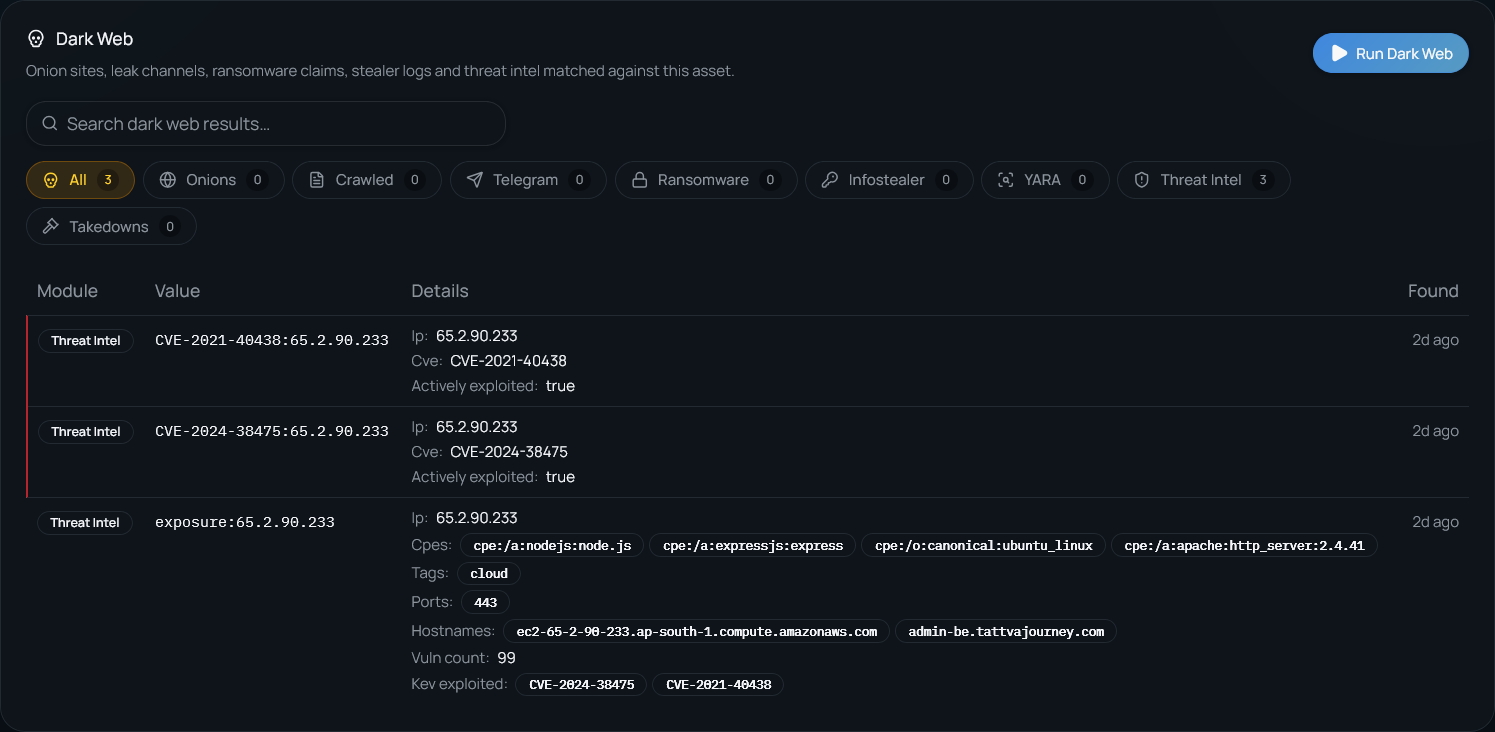
Dark web
Leaked credentials and mentions of your domains across paste sites, forums and breach dumps.
Brand
Look-alike and newly registered domains, flagged as they appear.
Cloud
Public buckets, exposed databases and misconfigured endpoints across your cloud assets.
Applications
Login portals, admin panels, outdated frameworks and exposed APIs on every web property.
- Know what reaches the internet.
- Know what exposes your data.
- Know what carries the most risk.
AI validation
Surfacia finds the doors. Our AI engineer tests whether they open.
What it adds
- Autonomous validation: AI agents test each weakness instead of leaving it as a maybe.
- Proof of concept: every confirmed finding comes with evidence you can reproduce.
- More, and more critical, findings: goes beyond automated scanning to cover the OWASP Top 10 and business-logic flaws.
- Web, API and cloud coverage: tests across your applications, APIs and cloud environment.
How it fits in
- Starts from Surfacia’s recon: it takes its targets from the interlinked recon data Surfacia already holds, so there is no re-discovery and no extra setup.
- Stays within agreed scope: testing is limited to the assets authorised for the engagement.
- Confirmed findings only: reports contain validated issues, not raw scanner noise.
No technical team needed on your side
You do not need security engineers to run it or to read its results. We operate the testing, and findings are reported with clear severity, evidence and remediation steps that your developers can act on directly.
Book a demo
See everything attackers can see.
Fix it before they do. Plans from $3,200 a year.